13.2.2 Connecting to Server via LDS
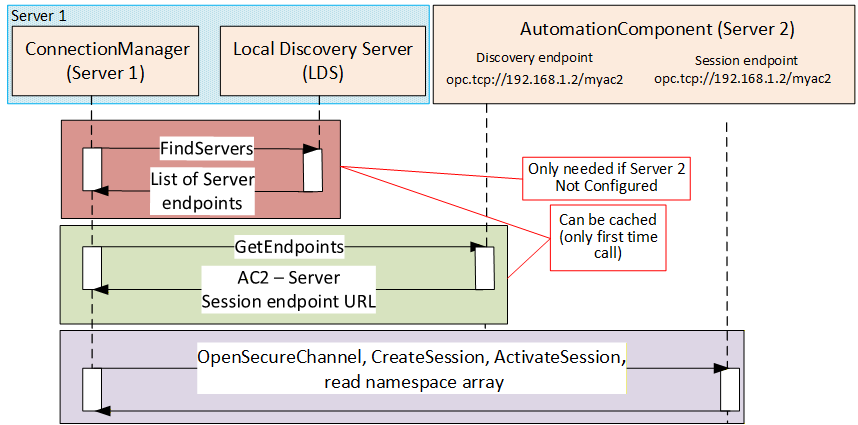
All devices expose a LocalDiscoveryServer (FindServersOnNetwork) or the Server directly exposes the Discovery Services (FindServers). The Server is located following the standard procedure as defined in OPC 10000-4, (i.e. using FindServers, GetEndpoints, OpenSecureChannel, CreateSession and ActivateSession) on the Server Address with the specified SecurityMode (see 9.2.2 for the description of the provided Server information).
If the Server is the same Server that the ConnectionManager resides on, the EstablishConnections Method may be invoked by vendor-specific means, and all portable node identifiers can be resolved locally.
The Session established by the ConnectionManager shall support the use of authentication and/or encryption. This includes:
Application authentication based on security mode and policy.
The use of Roles (this may require user authentication or specific ApplicationInstance certificates)
If SecurityPolicyUri contains empty or null string, the EndpointDescription on the Server with the highest SecurityLevel of the ones supported by the ConnectionManager and matching the requested SecurityMode (see 9.2.2) shall be chosen. If not empty of null string, the EndpointDescription matching the requested SecurityMode and SecurityPolicyUri (see 9.2.2) shall be chosen. The complete process, including NodeId resolution, is illustrated in Figure 65.